Tool to decrypt/encrypt Vigenere automatically. Vigenere cipher is a poly-alphabetic substitution system that use a key and a double-entry table.
Vigenere Cipher - dCode
Tag(s) : Poly-Alphabetic Cipher
dCode is free and its tools are a valuable help in games, maths, geocaching, puzzles and problems to solve every day!
A suggestion ? a feedback ? a bug ? an idea ? Write to dCode!
Vigenere Cipher
Vigenere Decoder
Vigenere Encoder
Answers to Questions (FAQ)
What is the Vigenère cipher? (Definition)
The Vigenère cipher is a polyalphabetic substitution cipher that uses a key (a word) to encrypt a message letter by letter.
Traditionally associated with Blaise de Vigenère, a 16th-century French diplomat and cryptographer, it employs a square (the Vigenère square, or tabula recta) that makes it possible to visualize the shifts applied to the letters based on the key.
How to encrypt with the Vigenère cipher?
The Vigenère cipher uses a key (and an alphabet).
Example: Encrypt the plaintext DCODE with the key CLE and the Latin alphabet ABCDEFGHIJKLMNOPQRSTUVWXYZ.
The Vigenère cipher can be described using 2 equivalent encryption methods (which give the same result).
METHOD 1: Vigenère encryption by letter addition
Encryption consists of adding the value of each key letter to the value of the corresponding plaintext letter.
— Assign each letter its alphabetical index, starting at 0: A=0,B=1,…,Z=25. Adding letters therefore means adding their numerical values.
— Calculate (plaintext-letter value + key-letter value) modulo 26. Since both values range from 0 to 25, subtract 26 if the sum is at least 26.
— Repeat the calculation for the remaining letters. Repeat the key until it covers the whole text: CLECLECLEC..
Example: Take the first plaintext letter, D (=3), and the first key letter, C (=2), and add them: 3+2=5. Continue with C (=2) and L (=11): 2+11=13, and so on. At the end of the key, start again from its beginning.
— For each number obtained (which must be a value between 0 and 25), match the letter with the same rank in the alphabet. The encrypted message is composed of the sequence of letters obtained.
Example:
| D | C | O | D | E | plaintext |
| 3 | 2 | 14 | 3 | 4 | values for each letter |
| C | L | E | C | L | repeated key |
| 2 | 11 | 4 | 2 | 11 | key-letter values |
| 5 | 13 | 18 | 5 | 15 | result of addition (modulo 26) |
| F | N | S | F | P | ciphertext |
METHOD 2: Vigenère encryption using a table
To encrypt with a double-entry table, use the following grid/matrix (with the alphabet ABCDEFGHIJKLMNOPQRSTUVWXYZ):
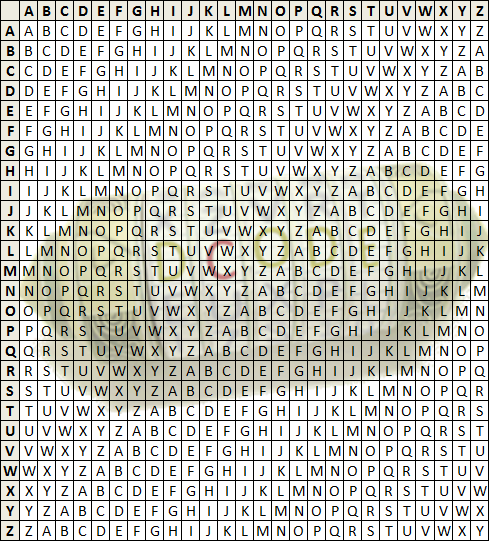
— Find the column for the plaintext letter and the row for the key letter; their intersection gives the ciphertext letter.
Example: The intersection of column D (the 4th column) and row C (the 3rd row) gives the ciphertext letter F.
— Repeat with the next message letter and the next key letter. At the end of the key, start again from its beginning.
Example: FNSFP is the ciphertext.
How to decrypt the Vigenère cipher?
Vigenère decryption requires a key (and an alphabet).
Example: Decrypt the message FNSFP with the key CLE and the Latin alphabet ABCDEFGHIJKLMNOPQRSTUVWXYZ.
Vigenère decryption can be described using 2 equivalent methods (which give the same result).
METHOD 1: Vigenère decryption by letter subtraction
Decryption consists of subtracting each key-letter value from the corresponding ciphertext-letter value.
— Assign each letter its alphabetical index, starting at 0: 0=A,1=B,…,25=Z. Subtracting letters therefore means subtracting their numerical values.
— Calculate (ciphertext-letter value − key-letter value) modulo 26. If the result is negative, add 26.
— Repeat the calculation for the remaining letters. Repeat the key until it covers the whole text: CLECLEC..
Example: Take the first ciphertext letter, F (=5), and the first key letter, C (=2), then calculate 5−2=3. The letter with index 3 is D.
— For each number obtained (which must be a value between 0 and 25), match the letter having the same rank in the alphabet. The plaintext is composed of the sequence of letters obtained.
Example:
| F | N | S | F | P | ciphertext |
| 5 | 13 | 18 | 5 | 15 | ciphertext-letter values |
| C | L | E | C | L | repeated key |
| 2 | 11 | 4 | 2 | 11 | key-letter values |
| 3 | 2 | 14 | 3 | 4 | result of subtraction (modulo 26) |
| D | C | O | D | E | plaintext |
METHOD 2: Vigenère decryption using a table
To decrypt with a double-entry square table, use the following grid/matrix (with the alphabet ABCDEFGHIJKLMNOPQRSTUVWXYZ):
— Find the row for the key letter (left column), then scan across it to find the ciphertext letter. The plaintext letter is the heading at the top of that column.
Example: The key letter C corresponds to row 3. In that row, F appears in column D, so the first plaintext letter is D.
— Repeat with the next ciphertext letter and the next key letter. At the end of the key, start again from its beginning.
Example: DCODE is the plaintext.
How to recognize Vigenère ciphertext?
The index of coincidence of a ciphertext encrypted with a repeating-key Vigenère cipher often tends towards that of random text (about 0.0385 for a 26-letter alphabet), but its value depends on the message and key length.
The French phrase “À l'aise, Blaise” may allude to Blaise de Vigenère's first name.
References to France or to Blaise de Vigenère's French nationality may be clues.
“Le chiffre indéchiffrable” (“the indecipherable cipher”) is a historical nickname associated with the Vigenère cipher, once considered very difficult to break.
Tabula recta is the Latin expression used for the alphabet table in the Vigenère cipher.
How to break the Vigenère cipher without knowing the key?
Cryptanalysis of the Vigenère cipher without knowing the key usually begins by estimating the key length using statistical methods. Frequency analysis can then be used to estimate each key letter.
KASISKI TEST
The Kasiski examination, published by Friedrich Kasiski in 1863 and anticipated by Charles Babbage, helps estimate the length of the encryption key. It is based on the observation that, in a ciphertext encrypted with a repeated key, repeated plaintext sequences that begin at positions aligned with the same key letters are likely to produce repeated ciphertext sequences.
The Kasiski test consists of identifying repeated sequences in the ciphertext and measuring the distance, in letters, between their occurrences. The common divisors of the distances obtained correspond to possible lengths for the key.
Example: ABC appears three times in the message ABCXYZABCKLMNOPQRSABC. The occurrences of ABC start at positions 0, 6 and 18. The pairwise distances from these positions are 6, 12 and 18 (possible multiples of the key length). Their common non-trivial divisors include 2, 3 and 6, so these are candidate key lengths that should be checked using other tests.
CALCULATION OF THE COINCIDENCE INDEX
To test a candidate key length N, split the ciphertext into N subsequences: the first contains letters at positions 0, N, 2N, and so on; the second contains those at positions 1, N+1, 2N+1, and so on. Calculate the index of coincidence for each subsequence and take the average. If N is the key length, each subsequence has been encrypted with a fixed shift, so its index of coincidence tends towards that of the plaintext language, especially for sufficiently long messages.
Once the length of the key is determined, it is possible to break the Vigenère cipher using frequency analysis. This method is based on the predictable distribution of letters in a given language (such as the high frequency of letters like E, T, A or O in English and E, A, S or I in French).
— Split the ciphertext into N subsequences according to the letter positions modulo N; each subsequence groups letters encrypted with the same key letter.
— Analyze each subsequence independently: each corresponds to a Caesar cipher, that is, a monoalphabetic substitution with a fixed shift.
— Calculate the frequency of letters in the subtext (count how many times each letter appears) and compare these frequencies with the frequencies of letters in the target language. The goal is therefore to find the shift applied to each subtext and to deduce the letter corresponding to the shift.
— Once the shift of each subtext is determined, deduce the key or apply the inverse shift (in negative) to the coded text.
How to recover the key when both plaintext and ciphertext are known?
During encryption, the key-letter value is added to the plaintext-letter value, modulo 26. To recover the key from matching plaintext and ciphertext, subtract each plaintext-letter value from the corresponding ciphertext-letter value, modulo 26.
NB: This is equivalent to decrypting the ciphertext with the plaintext as the key. The result is the key repeated and truncated to the message length.
Example: The ciphertext is FNSFP and the known plaintext is DCODE. Using DCODE as the key to decrypt FNSFP gives CLECL, which is the key CLE repeated and truncated to five letters.
What are the variants of the Vigenère cipher?
The Vigenère cipher has inspired several variants and related devices:
— The Beaufort cipher: a variant in which encryption subtracts the plaintext value from the key value (modulo the alphabet size).
— The Gronsfeld cipher: a variant whose key consists of digits from 0 to 9, used as shifts.
— The Vernam cipher and the one-time pad (OTP): for an OTP, the key must be independent of the message, uniformly random, secret, at least as long as the plaintext, and used only once. These conditions provide unconditional security in the ideal model.
— The Vigenère autokey cipher: instead of repeating a short key indefinitely, the plaintext or ciphertext can be used to extend the key, depending on the variant. These methods are not equivalent to a one-time pad and remain vulnerable to cryptanalysis.
— Vigenère with a disordered alphabet: the alphabet in the square can be permuted, for example using a keyword or a random ordering see Quagmire cipher.
— Vigenère with a custom alphabet: another character set, symbols, or digits can be used.
— Vigenère with a dynamic key: the key can change after certain characters or according to predefined rules.
— The Saint-Cyr slide rule: a mechanical device that applies Vigenère shifts using a fixed strip and a sliding double alphabet.
How to choose the encryption key?
The repeating-key Vigenère cipher is not secure for protecting sensitive information: statistical analysis can exploit the key's periodicity. A longer key may make analysis more difficult, but length alone does not guarantee security.
Unconditional security is achieved with a one-time pad (OTP) only if the key is secret, independent of the message, uniformly random, at least as long as the plaintext, and never reused. Reusing the same key for two messages compromises this security property.
What is the running-key Vigenère cipher?
The running-key variant uses a key as long as the message, often taken from a book or another text. Because this key is not periodic by construction, the classic Kasiski test is less directly applicable, but the system remains vulnerable to attacks using probable words, the key text, or character frequencies.
If the key consists of truly random characters that are independent of the message, secret, at least as long as the plaintext, and used only once, the system is a one-time pad (Vernam cipher) and provides unconditional security in the ideal model.
What is the keyed-alphabet Vigenère cipher?
Using a permuted alphabet, or a key that modifies the standard Latin alphabet, can make frequency analysis more complex. However, this does not by itself guarantee resistance to classical attacks, especially when the key is repeated. See the Quagmire cipher and its variants.
What are the advantages of the Vigenère cipher over the Caesar cipher?
The Caesar cipher is equivalent to a Vigenère cipher whose one-letter key is repeated throughout the message. With a longer repeating key, the same plaintext letter can be encrypted in different ways depending on its position. Whole-text frequency analysis is therefore less effective, but statistical attacks remain possible.
What is the Saint-Cyr slide rule?
The Saint-Cyr slide rule is an instrument that facilitates manual encryption and decryption using the Vigenère method. The fixed part bears one alphabet, while the sliding part generally bears the alphabet repeated twice.
To encrypt a letter, move the slider so that the key letter is positioned under the A of the fixed alphabet. Then read the letter on the sliding part directly below the plaintext letter shown on the fixed part.
Why is it called the Vigenère cipher?
The Vigenère cipher is named after Blaise de Vigenère, a 16th-century French diplomat and cryptographer (1523–1596), although he did not invent the repeating-key system now known by his name.
In his 1586 work Traicté des chiffres, ou secretes manieres d'escrire, Vigenère described, among other things, an autokey method. A reprinted edition is referenced under https://www.amazon.com/gp/product/285707798X?tag=dcodefr-21.
The Italian cryptographer Giovan Battista Bellaso had described a keyword-controlled polyalphabetic system in 1553; the cipher's history therefore involves a gradual and mistaken attribution to Vigenère.
When did the Vigenère cipher appear?
Blaise de Vigenère published a treatise on ciphers in 1586, including an autokey method, but the repeating-key polyalphabetic system now called the Vigenère cipher is misattributed to him. Giovan Battista Bellaso had described a related keyword-based system as early as 1553. A reprint of Vigenère's treatise is referenced under https://www.amazon.com/gp/product/285707798X?tag=dcodefr-21.
Source code
dCode retains ownership of the "Vigenere Cipher" source code. Any algorithm for the "Vigenere Cipher" algorithm, applet or snippet or script (converter, solver, encryption / decryption, encoding / decoding, ciphering / deciphering, breaker, translator), or any "Vigenere Cipher" functions (calculate, convert, solve, decrypt / encrypt, decipher / cipher, decode / encode, translate) written in any informatic language (Python, Java, PHP, C#, Javascript, Matlab, etc.) or any database download or API access for "Vigenere Cipher" or any other element are not public (except explicit open source licence). Same with the download for offline use on PC, mobile, tablet, iPhone or Android app.
Reminder: dCode is an educational and teaching resource, accessible online for free and for everyone.
Cite dCode
The content of the page "Vigenere Cipher" and its results may be freely copied and reused, including for commercial purposes, provided that dCode.fr is cited as the source (Creative Commons CC-BY free distribution license).
Exporting the results is free and can be done simply by clicking on the export icons ⤓ (.csv or .txt format) or ⧉ (copy and paste).
To cite dCode.fr on another website, use the link:
In a scientific article or book, the recommended bibliographic citation is: Vigenere Cipher on dCode.fr [online website], retrieved on 2026-11-17,


- Vigenere Decoder
- Vigenere Encoder
- What is the Vigenère cipher? (Definition)
- How to encrypt with the Vigenère cipher?
- How to decrypt the Vigenère cipher?
- How to recognize Vigenère ciphertext?
- How to break the Vigenère cipher without knowing the key?
- How to recover the key when both plaintext and ciphertext are known?
- What are the variants of the Vigenère cipher?
- How to choose the encryption key?
- What is the running-key Vigenère cipher?
- What is the keyed-alphabet Vigenère cipher?
- What are the advantages of the Vigenère cipher over the Caesar cipher?
- What is the Saint-Cyr slide rule?
- Why is it called the Vigenère cipher?
- When did the Vigenère cipher appear?